





Chief Information Security Officer
Aligns cybersecurity risk management with enterprise governance and compliance goals.
Explore the Chief Information Security Officer rolearrow_forwardarrow_forwardBenefit statement
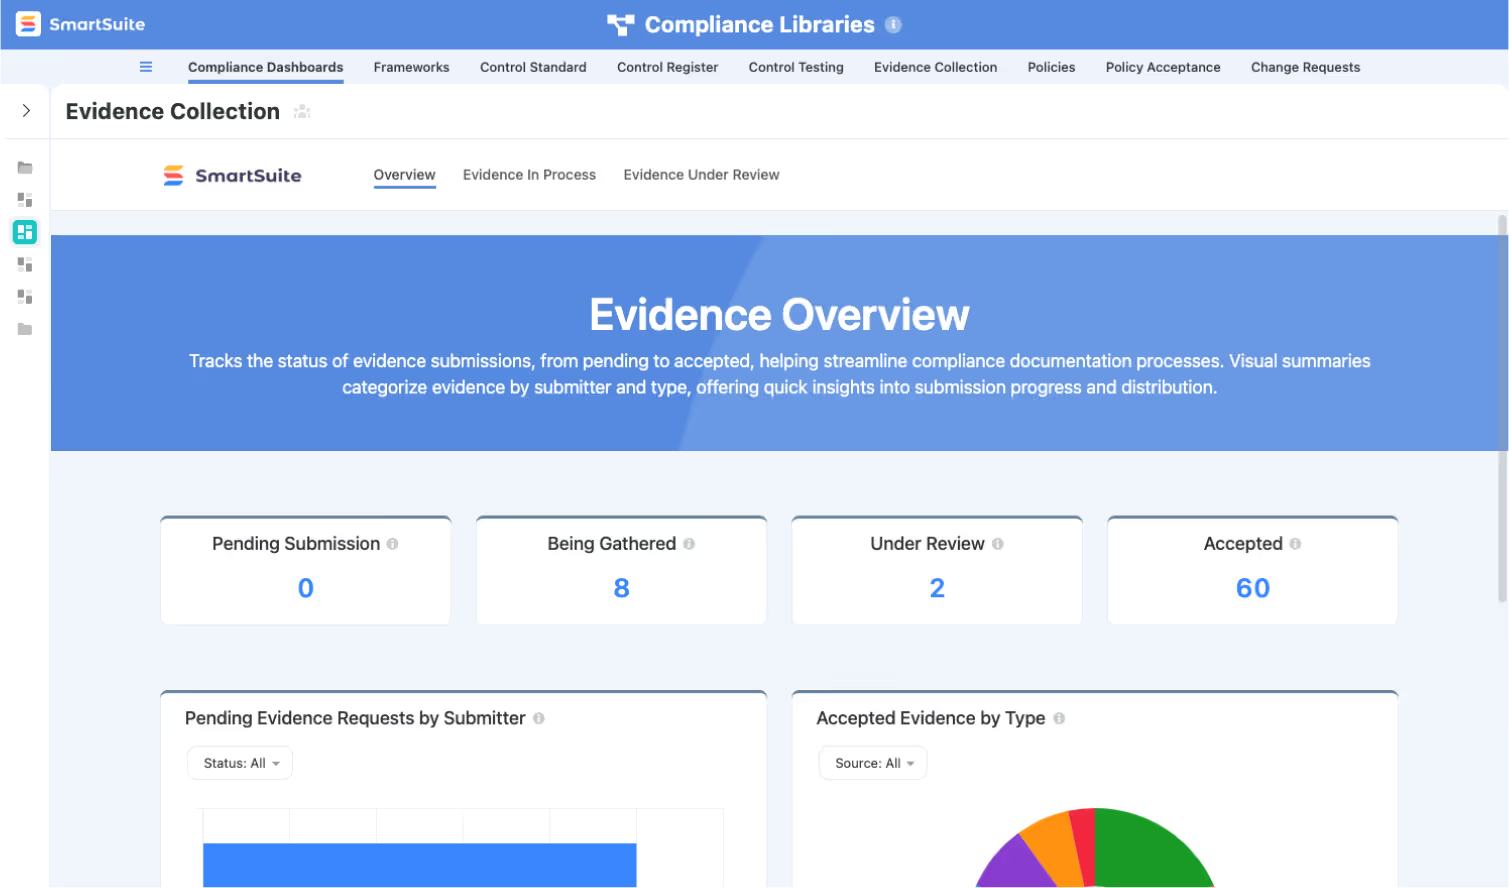
Cuts audit and security evidence preparation time by 40% through automated framework mapping (NIST, SOC 2, ISO 27001) and centralized control documentation that eliminates manual collection and versioning.arrow_forwardBenefit source
Validated by Gartner Cyber GRC Market Guide, 2024: automated evidence management reduced manual collection time by 35–45%.
How they use the Cyber & IT Risk suite
Cyber risk oversight
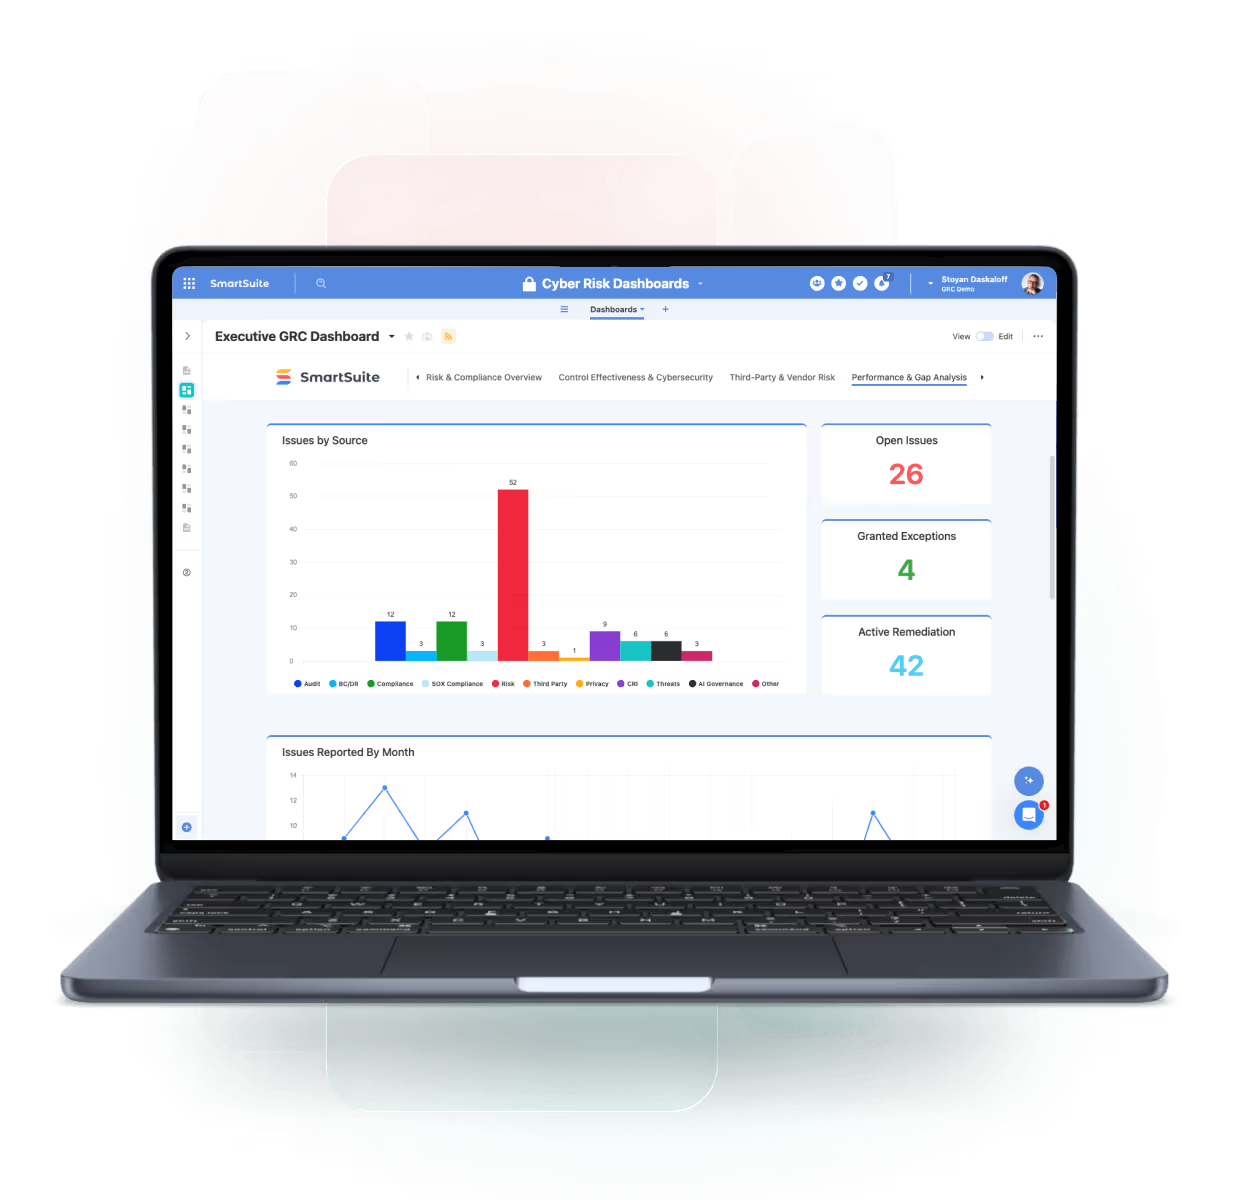
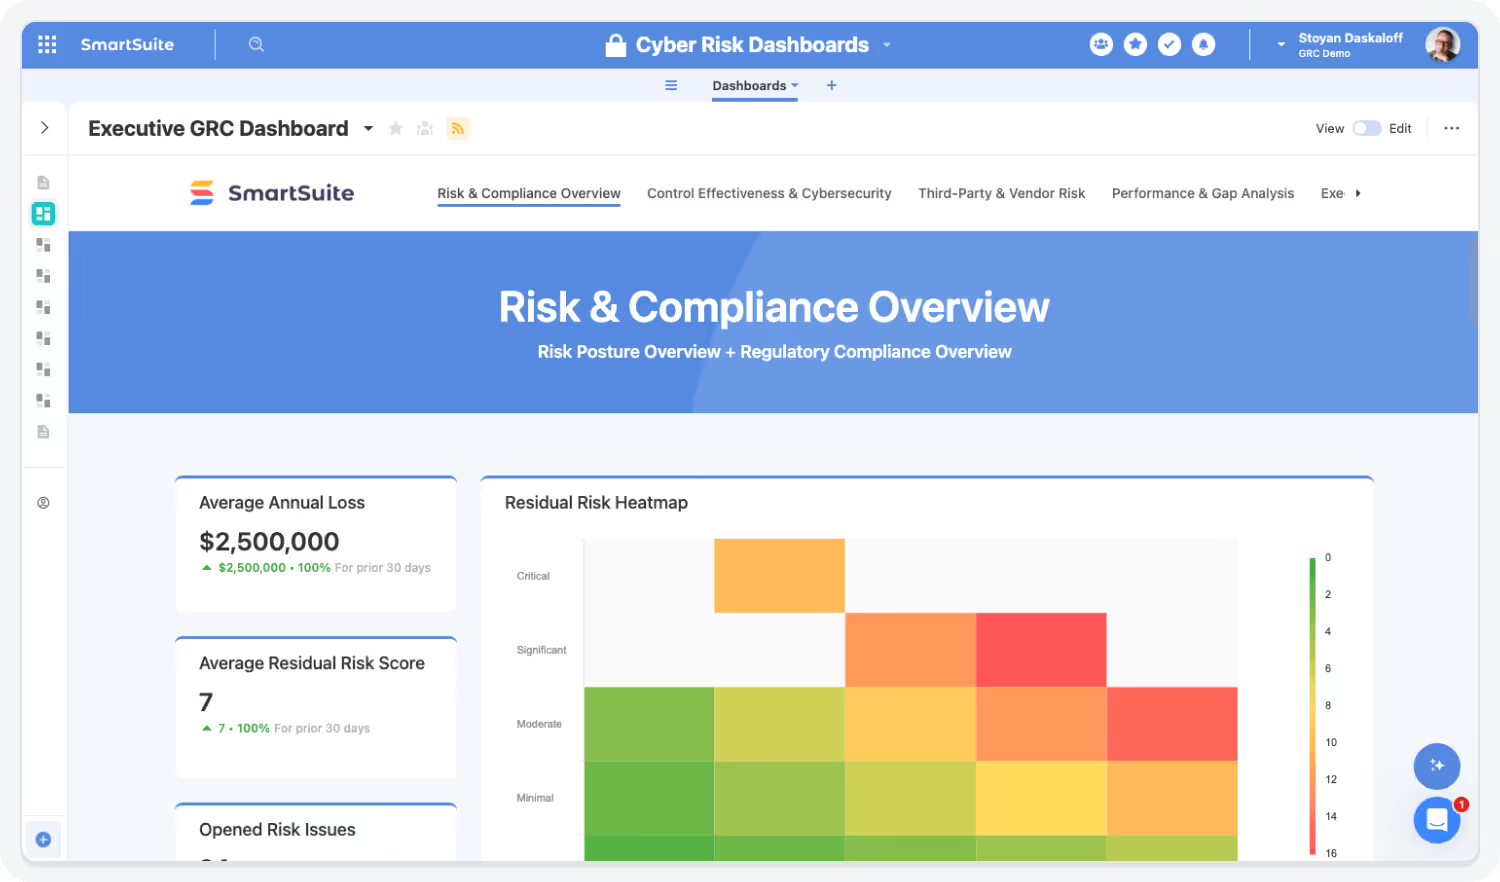
Tracks IT and cyber risks with visual dashboards linked to remediation activities.
Control governance
Maps security controls to frameworks like NIST or SOC 2 for streamlined evidence tracking.
Executive reporting
Provides real-time updates to leadership on security posture and control effectiveness.