

Are you looking for third-party risk management software to centralize vendor data, automate due diligence and risk scoring, ensure regulatory compliance, and/or continuously monitor suppliers?
A good third-party risk management software can continuously monitor vendors, automate due diligence and risk scoring, prioritize high-risk relationships for remediation, and produce audit-ready evidence.
In this buyer guide, I’ll cover the 10 best third-party risk management tools that can help you define risk templates, scoring criteria, control weightings, and playbooks per vendor type or criticality.
Key takeaways
- SmartSuite offers the best third-party risk management software with its all-in-one risk management capabilities, no-code automation builder, and pre-built vendor risk templates.
- Enterprise-grade tools like Diligent, OneTrust, and IBM OpenPages are ideal for large organizations that need deep regulatory mapping, audit readiness, and AI-powered governance.
- On the other hand, there are tools like StandardFusion, SAI360, and AuditBoard that can help mid-sized companies streamline vendor assessments, unify compliance, and stay audit-ready without heavyweight complexity.
Before we begin, I wanted to go over some of the factors to consider when you’re evaluating third-party risk management solutions:
What are the factors to consider when evaluating third-party risk management tools?
The main factors to consider in third-party risk management software include coverage of the full vendor risk lifecycle, integrations, workflow flexibility, and how audit-ready you can be with it.
Let’s dive deeper into each one of them: ⬇️
#1: Coverage of the full vendor risk lifecycle
The platform should support the entire vendor lifecycle, from onboarding and initial due diligence through ongoing monitoring, issue remediation, and offboarding.
Look for built-in assessment templates, automated evidence collection, and the ability to track corrective actions and remediation deadlines.
💡 If your program requires continuous monitoring (e.g., threat intelligence, financial health, or regulatory watchlists), confirm that those feeds and alerting capabilities are native or easily integrated.
#2: Integration, data sources, and automation
Risk programs rely on data flowing in from many systems, so evaluate the product’s integrations (APIs, SSO, GRC, procurement, ERP, SIEM, and ticketing/ITSM).
Ask whether it can automatically ingest questionnaires, evidence, security scans, and third-party alerts; manual uploads quickly become unscalable.
Also, check workflow automation: automated risk scoring, reassessment triggers, escalation paths, and remediation task creation save time and reduce human error.
#3: Risk modelling, customization, and workflow flexibility
The tool should let you define risk templates, scoring criteria, control weightings, and playbooks per vendor type or criticality.
Customizable workflows and role-based approvals are essential so legal, security, procurement, and business owners see only what they need and can act without bottlenecks.
💡 Scalability matters too if you’re an enterprise: ensure the product can handle thousands of vendors, varied assessment cadences, and different SLAs as your program grows.
#4: Reporting, auditability, and evidence management
Regulators and auditors will want clear evidence trails, immutable audit logs, and easy exports of assessments, remediation actions, and approvals.
Dashboards and reporting should enable you to slice risk by business unit, vendor criticality, contractual obligations, and open remediation items, providing leadership with concise, actionable views.
Your team should check whether the product supports templated executive reports, scheduled exports, and ad-hoc queries without heavy professional services.
➡️ Pro Tip: Good evidence management (timestamped docs, versioning, and secure storage) turns a GRC tool into a defensible record during incidents or audits.
What are the best third-party risk management platforms on the market?
The best third-party risk management platforms on the market include SmartSuite with its all-in-one risk management capabilities, intuitive interface and affordable pricing structure, as well as Diligent and OneTrust.
Here’s a comprehensive breakdown:
#1: SmartSuite: Best for banks and credit unions looking to centralize vendor risk, automate compliance, and launch third-party risk management workflows in days with no-code automation and pre-built templates.
#2: Diligent: Best for compliance teams needing board-level governance, enterprise policy oversight, and AI-powered regulatory insights.
#3: OneTrust: Best for enterprises seeking to unify privacy, security, and GRC while automating vendor assessments and regulatory compliance across 50+ frameworks.
#4: LogicGate: Best for organizations that need customizable workflows and AI-driven insights to automate vendor onboarding, risk scoring, and remediation playbooks.
#5: IBM OpenPages: Best for enterprises requiring AI-powered risk analytics, deep regulatory mapping, and scalable vendor lifecycle management.
#6: StandardFusion: Best for mid-market organizations looking for a straightforward, user-friendly platform with control libraries, evidence collection, and vendor assessments.
#7: SAI360: Best for companies that want an enterprise-wide, customizable system unifying risk, compliance, and ethics management with extensive pre-mapped frameworks.
#8: MetricStream: Best for large enterprises managing global vendor risk with AI-powered insights, deep audit integration, and supplier lifecycle management.
#9: ServiceNow: Best for enterprises wanting integrated vendor risk management embedded directly into ITSM and security operations.
#10: AuditBoard: Best for audit and risk teams needing strong evidence workflows, pre-built frameworks, and clear visibility into vendor control testing and remediation.
#1: SmartSuite
SmartSuite offers the best third-party risk management software on the market for banks and credit unions with our modern, no-code project management platform.
Our GRC software gives you a single, flexible workspace to catalogue vendors, run periodic assessments, automate contract and control workflows, score and monitor vendor risk, and link incidents to vendor assets without heavy IT involvement.

💡 We have recently partnered with the Cyber Risk Institute to deliver a CRI profile for U.S. Banks' compliance needs.
Let’s go over the functionality that makes SmartSuite the best choice for compliance teams looking for a third-party risk management solution: 👇
All-In-One Risk Management Software
Our no-code, easy-to-use platform empowers compliance managers and CISOs to automate all risk management processes with ease.

Here are the use cases that you’ll get with SmartSuite:
- Create reports and dynamic dashboards: Monitor executive views into your organization's overall risk profile with powerful charting and metrics widgets.

- Collaborate and respond to risks in real-time: Engage key stakeholders in a real-time discussion of potential threats or vulnerabilities.
Our software will also let you get instant updates when critical information is available.

- Automate policy creation, real-time approval, and control assessments: Streamline risk management by building an integrated program on a single platform.
- Keep risk and compliance data secure: Define your teams and manage access to information across all GRC practice areas.

- Integrate with your existing systems: Our GRC software lets you integrate with existing systems (ticketing, identity, procurement, CMDBs) and data to consolidate and centralize your data.
Your team will be able to:
- Pull vendor contract data from procurement systems or push assessment tasks into the ticketing system.
- Sync vendor asset inventories from CMDBs so risk assessments reflect the actual scope of access.
- Retrieve security telemetry or incident data into vendor records to automate risk reclassification.

- Monitor, measure and score: Create risk calculations and metrics to evaluate every aspect of risk.

- Policy management: It’s possible to establish a strong foundation from the get-go with streamlined and flexible policy management.
You’ll be able to assign ownership, manage revisions, and ensure your policies consistently align with key business initiatives and regulatory requirements.

- PSTOS Compliance Tracker: Designed for regulatory compliance and built on SmartSuite.
This solution focuses on data security as the core of compliance frameworks with services such as compliance readiness, virtual CISO, and IT security implementation.
Learn more about it from this webinar that we did on the topic:
Prioritize & Mitigate Risks
With SmartSuite, you can create a centralized risk register to effectively identify potential risks to your organization.
You will be able to properly assess threats and establish risk mitigation strategies inside SmartSuite.

Your team can ensure that the appropriate controls are in place and measure their effectiveness by evaluating risk indicators and displaying results in SmartSuite’s rollup reports and dashboards.
💡 Pro Tip: Teams that use our platform use automation to move tasks through defined workflow stages that comply with their policies and procedures.

We understand how crucial threat management is and the need to respond quickly to incidents.
SmartSuite lets you centralize incident response and threat mitigation by linking incidents to assets and organizational data to offer context during your investigations.
Your compliance team can also set up automation with our no-code automation builder to escalate critical events to make sure that your team is aware of active risks to your organization.

No-code automation to enforce process and reduce human error
SmartSuite's no-code automation builder provides you with a visual interface that makes it easy to respond to events and take action.
For TPRM, you can use automation to:
- Auto-assign assessment tasks when a vendor is onboarded.
- Escalate high-severity findings to the vendor owner and CISO when a score threshold is exceeded.
- Auto-create remediation tasks from failed control checks and move them through predefined workflow stages.
- Send reminders for expiring certificates, upcoming renewals, or overdue remediation.
💡 This removes a lot of operational friction: policies are enforced by workflow rather than memory or spreadsheets, which improves compliance and speeds up remediation.

Pre-Built Third-Party Risk Management Templates
SmartSuite’s third-party templates let you consolidate every vendor record into one place with fields for:
- Legal name, DBA, vendor type, location, line of business
- Contract info (start/renewal/termination dates), owners, SLAs
- Criticality/tier, data access levels, and assets the vendor touches
- Assessment history, findings, remediation plans, attachments (contracts, attestation docs)
➡️ Having all vendor facts, contracts, and assessment artefacts co-located removes the spreadsheet chaos and makes it possible to link vendor records directly into risk processes, dashboards, and automations.
Our general risk management template includes:
- Third-Party Risk, where you can view vendor profiles, vendor engagements, and build a vendor risk assessment sheet.
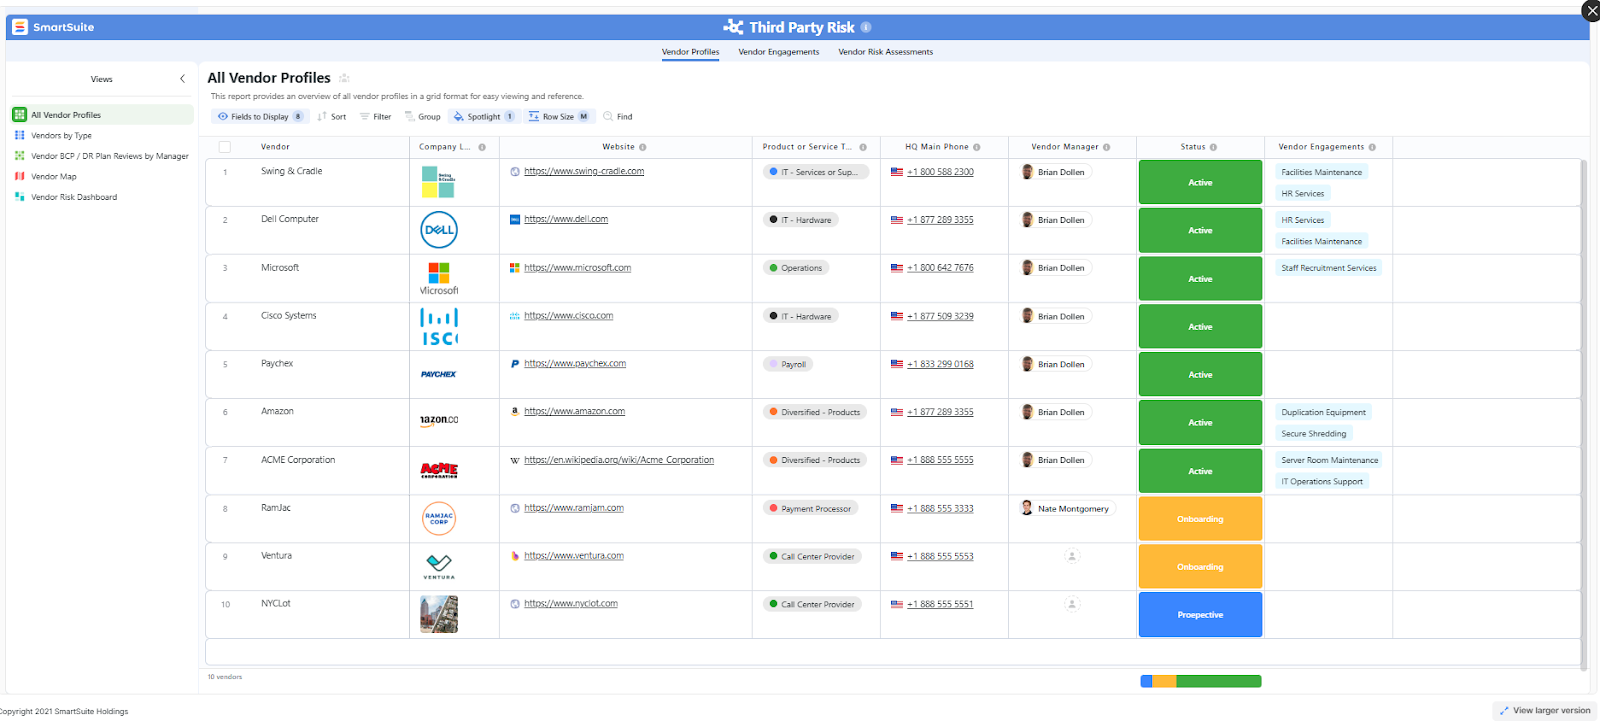
- Risk register, where you can break down the risks, the risk owner, the annual loss expectancy, risk event category, risk type, volatility, and status.

- Issue assessments, where you’ll be able to see a comprehensive breakdown of each risk.

- Action plans, where you can describe the actions (best practices) to mitigate the risks.

- A separate tab for control standards, your findings, exception requests, risk assessment by type, and risk assessment issues.

You can customize our risk management template here.
Alternatively, check out and customize our 14 other risk management templates for various use cases, such as contract management, policy management, and incident management.

Pricing
SmartSuite offers a free plan with access to 250+ automation actions, team collaboration, multi-dashboard views, and more.
There are four paid plans with a 14-day free trial (no CC required):
- Team: Starts at $12/user per month, including Gantt charts, timeline views, 5000 automation runs, and native time tracking.
- Professional: Starts at $30/user per month and adds two-factor authentication, Gmail & Outlook integrations, and unlimited editors.
- Enterprise: Starts at $45/user/month and includes access to audit logs, data loss prevention, and 50,000 monthly API calls.
- Signature: A customized plan tailored to your organization’s needs and team size with no predefined limits.

Pros & Cons
✅ A generous free plan that includes access to advanced features of the tool for up to 5 solutions.
✅ 15 out-of-the-box GRC templates for various use cases.
✅ Dynamic dashboards and reports that are easy to build and navigate, unlike some alternatives that require you to hire consultants to do it.
✅ All-in-one document and file management.
✅ You’ll be able to automate risk scoring, compliance tracking, audits, and vendor reviews.
✅ A modern solution with an intuitive user interface.
❌ Fewer native integrations when compared to other platforms in this list.
#2: Diligent
Best for: Compliance teams looking for board-level governance and enterprise policy oversight.
Similar to: Onspring, ArcherIRM.
Diligent excels at board-level governance and enterprise policy oversight, giving executives a consolidated view of vendor and third-party exposures.
It’s strong where compliance needs to be tied directly to governance and decision-making.
Features
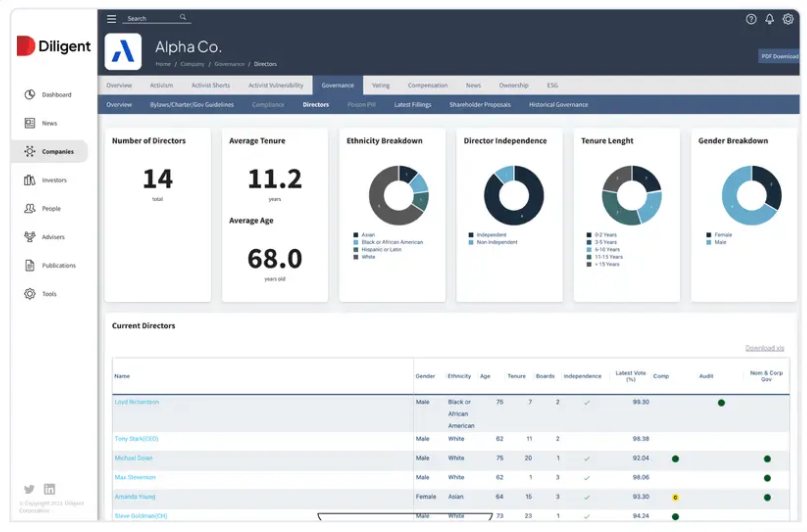
- Centralized vendor due diligence workflows that track onboarding, approvals, and remediation across business units.
- You can configure ongoing data tests and automate business process monitoring (e.g. internal control testing) to detect anomalies and maintain compliance in real-time.
- It’s possible to use scripted tasks in Python or ACL to automate data aggregation, testing, and remediation notifications.
Standout Feature: Diligent AI
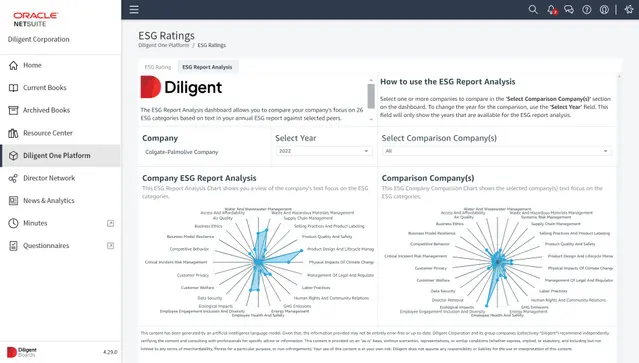
What stood out to me about Diligent is its AI assistant that helps you anticipate risk and stay compliant by generating summaries, mapping out regulatory requirements, and automatically benchmarking ESG and risk in real-time.
Pricing
There’s no official data on Diligent’s pricing plans; however, our team was able to find some reported numbers.
According to 3rd-party data from Vendr, the median buyer of Diligent spends $23,800/year for its solution, with the tool going up to $45,792/year.
Pros & Cons
✅ One centralized GRC system that aims to replace multiple tools and simplifies oversight across risk and audit workflows.
✅ Integration-rich, allowing you to create seamless workflows between tools.
✅ An AI-powered assistant that can help you boost productivity.
❌ A steep learning curve and long initial setup and onboarding times.
❌ The tool’s pricing can get expensive, which is why some users have been looking for Diligent alternatives.
#3: OneTrust
Best for: Enterprises looking to combine privacy, security, and GRC capabilities.
Similar to: ServiceNow.

OneTrust combines privacy, security, and GRC capabilities so vendor assessments, data-processing mapping, and regulatory requirements are handled in the same platform.
Its modular design makes it easy to expand TPRM controls as new regulations or risks emerge.
Features

- Automated vendor risk assessments and attestations mapped to privacy and regulatory frameworks.
- Connect compliance teams and departments via automated workflows and 200+ pre-built integrations.
- Map systems, data, and risks in one unified view: You can prioritize action with dynamic scoring and strategic impact insights.
- You can automatically generate the required controls and evidence tasks.
Standout Feature: Proprietary Shared Evidence Framework

OneTrust stood out to me with its functionality to collect evidence once and comply across 50+ frameworks with OneTrust’s shared evidence framework to help you eliminate duplicate data requests.
Pricing
OneTrust has different pricing plans for its 5 product lines, all of which have custom pricing:
- Consent & Preferences: Capture and activate consent, preferences, and first-party data across your user touchpoints.
- Privacy Automation: Simplify compliance, improve operational efficiency, and help your business better use personal data.
- Third-Party Management: Third-party risk management and the ability to fully manage your third-party lifecycle.
- Tech Risk & Compliance: Scale governance, risk, and compliance, and mature your risk program.
- AI Governance: Gain visibility and control over your AI technology and empower risk-based decisions.
➡️ You can review our OneTrust pricing guide, where I go over how much the tool really costs.

Pros & Cons
✅ Collect evidence and comply across 50+ frameworks with OneTrust’s shared evidence framework.
✅ Comprehensive range of integrations when compared to other competitors in this list.
✅ Monitor and manage your program with dynamic dashboards.
❌ The cost can be an issue for smaller companies, as it’s expensive, which is why some people have been looking for OneTrust alternatives.
❌ The UI has been described as outdated and not user-friendly by G2 reviews.
#4: LogicGate
Best for: Setting up dynamic questionnaires that automate onboarding, risk scoring, and issue escalation.
Similar to: ServiceNow GRC.

LogicGate’s low-code risk-orchestration engine lets teams model complex third-party processes and automate remediation playbooks without heavy IT support.
That flexibility makes it ideal for organizations that need bespoke workflows for vendor risk.
Features

- Customizable workflows and dynamic questionnaires that automate onboarding, risk scoring, and issue escalation.
- Centralized risk repository for visibility across governance, compliance, and third-party risks.
- Pre-built templates that your team can start with to automate compliance reporting, as well as audit trails.
Standout Feature: Spark AI

LogicGate offers AI-powered insights that help you predict risk and support your decision-making.
➡️ Spark AI also helps you generate executive summaries, which are ideal for busy CEOs looking for a quick update.
Pricing
LogicGate does not publicly disclose its pricing, so you’d have to book a personalized demo with their team to get a quote.
➡️ You can take a look at our LogicGate pricing review, where we found some reported numbers and also discuss whether it has good value for money.

Pros & Cons
✅ AI-driven insights that help you predict risk and support your decision-making.
✅ LogicGate Risk Cloud automates control follow-up tasks.
✅ Customers of the platform appreciate how responsive the customer service team has been.
❌ Some of LogicGate’s customers find the calculation functionality complicated, particularly with labels and percentages.
❌ The reporting features have limitations, which is why some users have been looking for LogicGate alternatives.
#5: IBM OpenPages
Best for: Connecting to enterprise data sources and reporting, so third-party exposures can be surfaced across business units
Similar to: SAI360.

IBM OpenPages delivers enterprise-grade GRC with strong risk taxonomy, regulatory mapping, and analytics, enabling organizations to manage vendor and third-party risk at scale.
It connects to enterprise data sources and reporting so third-party exposures can be surfaced across business units and regulatory regimes.
Features

- Centralized third-party risk register with configurable scoring, workflow automation, and regulatory mapping to manage vendor lifecycle, assessments, and remediation.
- Utilizes IBM Watson for natural language processing and machine learning (ML) to provide predictive analytics and automate classifications.
- Features a drag-and-drop workflow editor that helps you automate GRC processes to improve time-to-value and reduce manual effort.
Standout Feature: IBM Cognos Analytics (Predictive Insights)

IBM OpenPages stood out to me with its valuable insights into the state of risk across the organization, with its IBM Cognos Analytics for self-service data exploration.
Pricing
IBM OpenPage’s pricing can be a little confusing, but there are 4 ways to purchase the solution:
- As a SaaS solution: Essentials Edition starts at $3,300, and the Standard one starts at $6,050.
- As an On-cloud solution: the Single Solution starts at $6,250, and the Enterprise one starts at $9,000.
- As part of IBM Cloud Pak for Data: the Single Solution starts at $162,000, and the Solution Bundle starts at $207,000.
- As On-Premises: You need to contact their team for a quote.

Regardless of which package you opt for in the end, each one will include a core set of IBM OpenPages features, such as its AI features, workflow automation, integrated reports, etc.
Pros & Cons
✅ Scalable architecture that was designed to scale to tens of thousands of users.
✅ Enhances efficiency and accuracy through bespoke AI models and automated processes.
✅ Get valuable insights into the state of risk across the organization with IBM Cognos Analytics.
❌ The platform’s high implementation costs can make it prohibitive for SMEs.
❌ There are reported to be limited customization options, which is why some users have been looking for IBM OpenPages alternatives.
#6: StandardFusion
Best for: Organizations looking for straightforward control libraries, evidence collection, and vendor assessments.
Similar to: IBM OpenPages.

StandardFusion is a cloud-native, user-friendly GRC platform that’s built for quick deployment and practical vendor-risk workflows, making it attractive to mid-market and scaling teams.
The platform focuses on straightforward control libraries, evidence collection, and vendor assessments without heavyweight enterprise complexity.
Features

- Intuitive vendor risk assessments and control management with centralized evidence storage and attestation workflows to simplify third-party audits and ongoing monitoring.
- Enterprise Risk Management integration that lets you guide all GRC activities for strategic decision-making and risk mitigation.
- Centralized data and analytics for monitoring internal controls.
Standout Feature: Automated Workflows

What stood out to me about StandardFusion is its automated workflows that aim to streamline your GRC processes and reduce system complexity.
Pricing
StandardFusion does not currently disclose its pricing structure, so you’ll have to reach out to them to get a product demo and a quote.

Pros & Cons
✅ User-friendly user interface that is easy to navigate.
✅ Comprehensive control, monitoring, and risk management features.
✅ Consolidates multiple compliance frameworks (e.g., ISO 27001, SOC 2, GDPR, HIPAA, NIST) in one platform.
❌ Recurring task management and tracking can be difficult, according to G2 reviews.
❌ The platform’s annual price increases are a concern for smaller enterprises.
#7: SAI360
Best for: Companies looking to unify risk, compliance, and ethics management into one customizable platform.
Similar to: MetricStream.

SAI360 delivers broad GRC coverage with extensive compliance content and supplier risk modules tailored to regulated industries, supporting complex, jurisdictional requirements.
The platform is useful where compliance libraries and prescriptive assessments are needed for vendors.
Features

- 20+ GRC modules for enterprise risk, IT risk, third-party risk, internal audit, business continuity, policy, and incident management.
- Large compliance and supplier-risk content library coupled with automated assessments and remediation workflows.
- Built-in e-learning so your team can be well-prepared to meet regulatory demands.
- Pre-mapped frameworks and controls aligned with global regulations for faster deployment and easier compliance.
Standout Feature: Integrated GRC from Every Angle

SAI360 offers a holistic, enterprise-wide approach that can help you unify risk, compliance, and ethics management into one customizable system.
Pricing
SAI360 does not currently disclose its pricing, so you’d have to contact them to get a product demo and a quote.
However, we researched SAI360’s pricing and found some reported numbers, so do check out our guide on it.

Pros & Cons
✅ Best-in-class reporting, risk assessment, and operational efficiency for enterprises.
✅ A holistic approach that helps your team unify risk, compliance, and ethics management.
✅ 20+ ready-to-use GRC modules that you can get started with without having to set up the platform for months.
❌ The platform is described as outdated and difficult to manage by user reviews.
❌ Admins cannot easily modify fields or workflows, which has made some customers upset with the tool.
#8: MetricStream
Best for: Enterprises looking for an all-in-one platform to manage risk on a global scale.
Similar to: LogicGate, SAP GRC.

MetricStream scales for large enterprises, combining supplier lifecycle management with audit and control frameworks so vendor risks are managed across global operations.
The platform is built for organizations that need deep regulatory mapping and audit integration.
Features

- Standardized enterprise-wide risk management frameworks that come with advanced analytics and real-time reporting.
- Enterprise supplier-lifecycle management that ties vendor risk to audits, controls, and regulatory requirements.
- Cyber risk intelligence and unified IT risk management to proactively address threats and ensure regulatory compliance.
- Centralized third-party risk management, including performance tracking and business continuity risk assessment.
Standout Feature: AI-powered insights (AiSPIRE)

MetricStream stood out to me with its AI-powered insights solution, AiSPIRE, which can be used for predictive risk identification, duplicate control detection, and cognitive recommendations.
Pricing
MetricStream does not disclose its pricing structure, so you’d have to contact them to get a product demo and a quote.
However, our team did some digging and created an in-depth MetricStream pricing guide, where I found some reported numbers:
- Small enterprise deployment costs between $75,000 - $150,000 per year.
- Medium enterprise deployment costs between $250,000 - $500,000 per year.
- Large enterprise deployment can cost between $750,000 - $1,000,000 per year.

Pros & Cons
✅ Real-time cyber risk intelligence capabilities.
✅ Advanced analytics alongside real-time reporting.
✅ An AI-powered insights tool, AiSPIRE, that you can use for predictive risk identification.
❌ The platform’s pricing structure is not SME-friendly, according to user reviews.
❌ The interface can be hard to navigate, which is why some users look for MetricStream alternatives.
#9: ServiceNow
Best for: Enterprises looking for integrated risk management and compliance automation.
Similar to: SAI360.

ServiceNow embeds vendor risk into ITSM and security operations on the Now Platform, enabling real-time workflows, ticketing, and remediation tied to vendor incidents.
That makes it powerful for organizations that want vendor risk visible where IT and security teams already work.
Features

- Eliminate silos by centralizing enterprise risk and compliance data into one source.
- Workflow-driven vendor risk management integrated with ITSM, security incidents, and the CMDB for contextual impact analysis.
- The GRC solution operates on ServiceNow’s Now Platform, which enables seamless data sharing and real-time collaboration across all GRC products.
- 3rd party risk management that helps you identify and mitigate risks from external vendors and partners.
➡️ You can learn more about ServiceNow in our comprehensive ServiceNow review.
Standout Feature: AI-Powered Actionable Insights

ServiceNow stood out to me with its AI-powered actionable insights that help you accelerate decision-making with predictive analytics and process optimization.
Pricing
ServiceNow’s pricing is not disclosed, so you’d have to book a demo with their team.
We found ServiceNow customer and public reviews, which show that the average cost of ServiceNow contracts can range between $50,000 and $500,000 annually.
Apparently, the pricing structure depends on the number of licenses, features, and other configuration requirements.

Pros & Cons
✅ Comprehensive risk, audit, and compliance management features.
✅ Real-time risk monitoring and prioritization.
✅ A comprehensive range of native integrations with other tools.
❌ Steep learning curve and complexity, unlike some ServiceNow alternatives.
❌ Training, skills development, and ongoing support can be costly.
#10: AuditBoard
Best for: Companies looking to streamline control testing and remediation tracking.
Similar to: LogicGate.

AuditBoard is audit-centric, giving audit and risk teams end-to-end visibility into third-party controls, findings, and remediation with strong evidence and testing workflows.
It’s ideal where auditability and clear control testing of vendors are priorities.
Features

- A comprehensive view of organizational risk that connects your audit, risk, and compliance teams.
- Audit-focused vendor risk assessments and evidence management that streamline control testing and remediation tracking.
- Customizable reports and pre-built dashboards that can help your compliance team uncover insights, track trends, and support data-driven decisions.
- Integrated workflows and APIs that help you streamline data collection and task management through integrations.
Standout Feature: Pre-Built 30+ Frameworks

AuditBoard offers access to its preloaded library of 30+ frameworks (including SOC 2, ISO 27001, and GDPR) to help you stay audit-ready as your organization scales.
Pricing
AuditBoard has not yet disclosed its pricing, so you’d have to contact them to book a demo and get a quote.

Pros & Cons
✅ Access to a single view of organizational risk.
✅ Modern interface with good AI capabilities.
✅ Access to a preloaded library of 30+ frameworks to help you stay ready for audits.
❌ The average contract value of the tool is around $42,775/year, according to insiders, which is why some people have been looking for AuditBoard alternatives.
❌ Some users of the platform find it difficult to use.
Get Started With SmartSuite & Our Ready-To-Use Third-Party Risk Management Templates For Free
That was it from our list of the 10 best third-party risk management platforms on the market in 2026 for compliance teams looking for a solution.
If your team needs to centralize vendor risk, shorten time-to-remediation, and keep stakeholders informed, try SmartSuite with its free plan and pre-built vendor-risk templates.
SmartSuite offers straightforward configuration, centralized evidence collection, and workflow-driven assessments to help teams build repeatable vendor onboarding and monitoring playbooks, assign ownership, and track remediation from initial assessment through ongoing monitoring.
Here’s what's in it for your team when you try SmartSuite:
- Access to a generous free plan with features including multi-board views (Kanban, Chart, Map, Timeline, Card, and Calendar), 100 automations/month, and 40+ field types, including formula and linked record fields.
- No-code automation builder to set up to 500,000 trigger/action workflows.
- Built-in productivity tools, including time tracking, status tracking, and checklists.
- Team collaboration and planning tools such as whiteboards and SmartSuite docs.
- Resource management across projects and teams.
- 40+ field types, including the option to add your custom fields.
Sign up for a free plan to test the water or get a 14-day free trial to explore all its amazing features.
Or, if you’d like to talk to our team of experts, schedule a demo.
Read More
- 10 Best Riskonnect Alternatives For GRC
- Riskonnect Pricing: Is It Worth It
- Atera Pricing: Is It Worth It
- BMC Helix Pricing: Is It Worth It
SmartSuite provides work platform for standardizing workflows in the following areas:
- Governance, Risk & Compliance
- IT & Service Ops
- Project / Portfolio Management
- Business Operations