



Workspace Secrets — Store API Keys Once, Never Paste Them in Code
Keep the API keys, tokens, passwords, and connection strings your scripts and integrations use in one admin-controlled store—referenced by name, encrypted at rest, rotated in one place, and revealed only with a recorded trail.
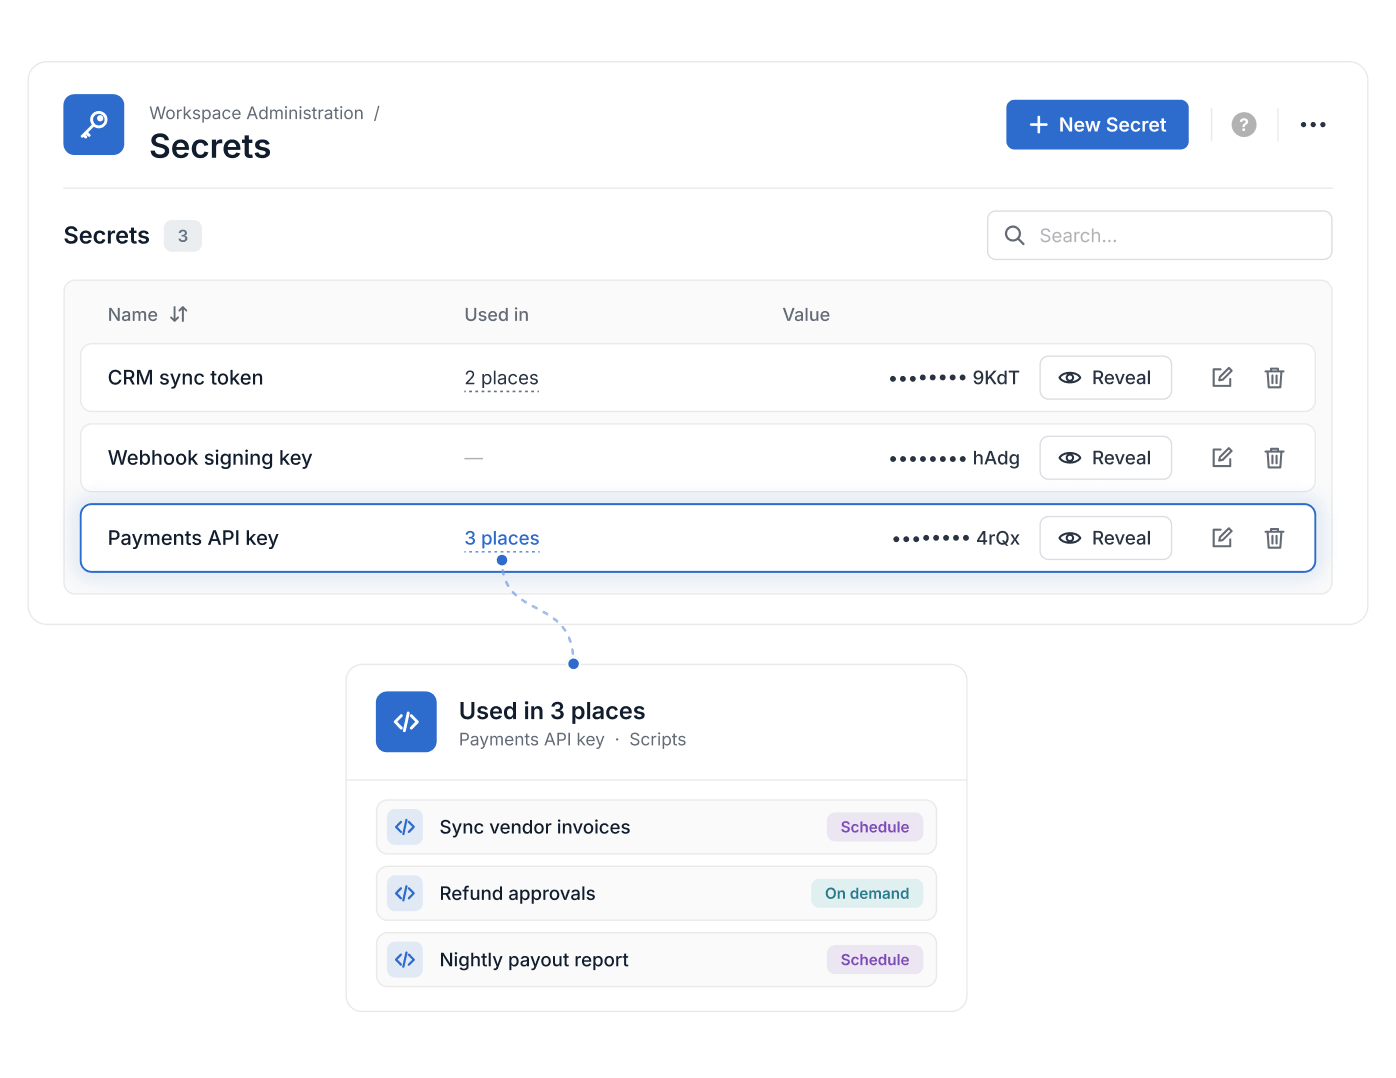
- Secrets live on their own page under Workspace Administration, directly below Script Engine.
- Each secret has a unique name and a value such as an API key, token or password; scripts reference the name, so the value never appears in code.
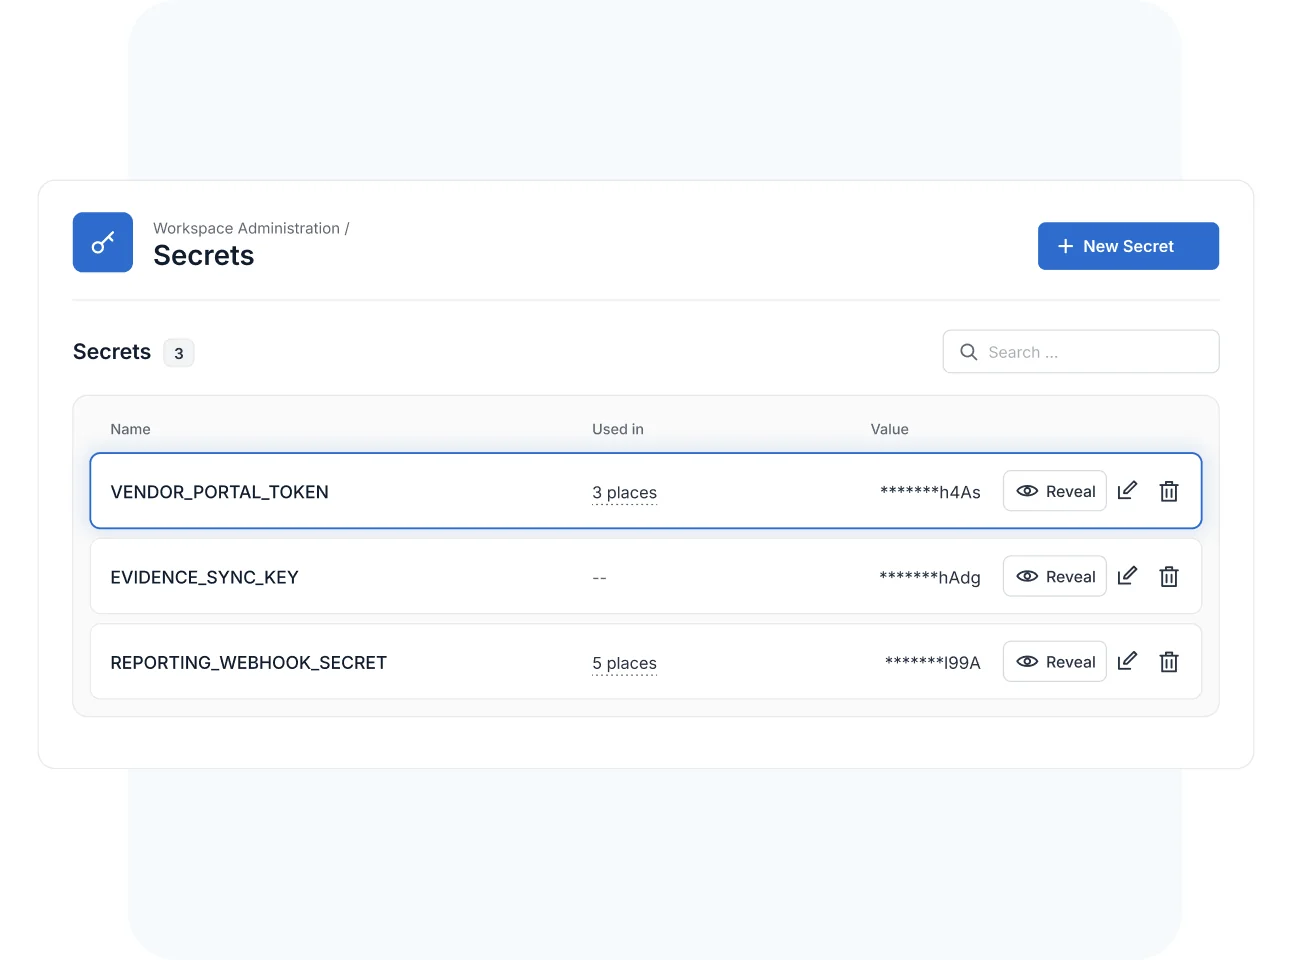
- Values are encrypted on save, masked to their last four characters in the list, and never read back except through the Reveal action.
- A Used in column shows how many places reference a secret, and renaming a secret does not break scripts that use it.
What Is Workspace Secrets?
Workspace Secrets is SmartSuite's admin-controlled store for the sensitive values your scripts and integrations depend on—API keys, access tokens, passwords, and connection strings—managed from the Secrets page under Workspace Administration. Administrators create a secret once, scripts reference it by name and receive the value at run time, and the value itself is encrypted, masked in every list, and shown in full only through a recorded Reveal action. It helps IT and security teams keep credentials out of code—centralizing rotation, usage tracking, and retirement in one place.
Central Storage
Enter Each AI Provider Key Once in the AI Control Center
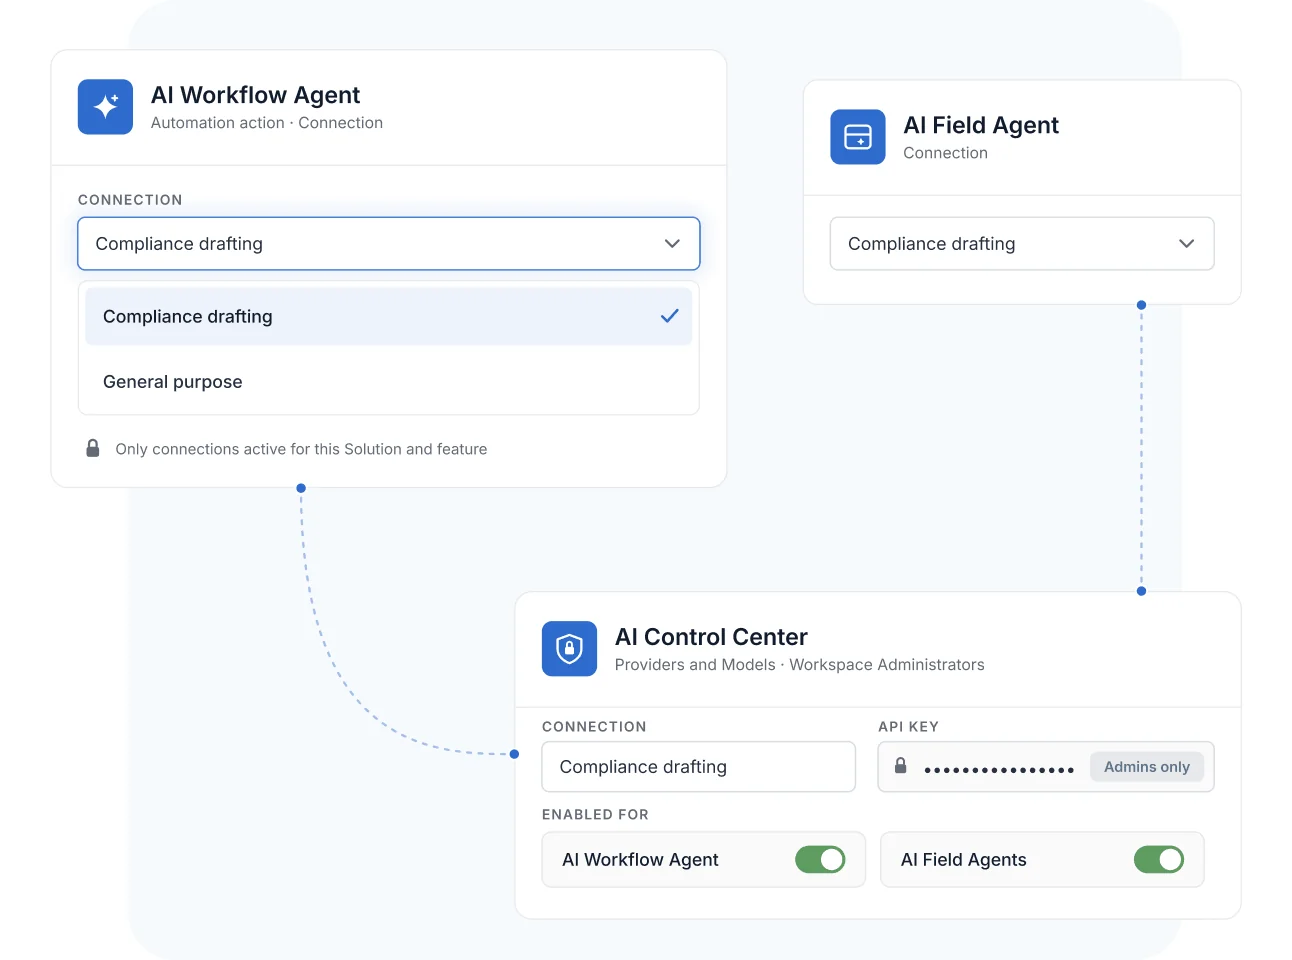
All of a Workspace's AI connections live in one central place, restricted to Workspace Administrators. Setting one up takes a single pass: pick the provider and model, paste in the API key, then name and describe the connection so its purpose is clear to every admin who reviews it later.
Supported providers span the major LLM ecosystem—OpenAI, Anthropic, Google Gemini, Amazon Bedrock, Azure OpenAI, Perplexity AI, IBM watsonx, and xAI—so bring-your-own-model strategies run through one governed door.
Point-of-Use Protection
Keep Keys Invisible Where AI Features Consume Them
Downstream consumers—AI Workflow Agent and AI Field Agent automation actions—select from a dropdown of only the connections active for that Solution and feature. The underlying key is never re-entered, pasted into a builder, or exposed at the point of use.
When a key must be rotated or a feature shut down, admins change it once centrally—every workflow that uses the connection follows, with nothing to hunt down.
Workspace Secrets
Credentials pasted into scripts are the finding every access review turns up. Workspace Secrets keeps the keys behind GRC integrations in one governed store—while teams keep building freely.
Scope an enterprise-grade model connection to the risk and compliance Solutions alone, so AI drafting on sensitive registers runs only through the provider your security review approved.
Point access reviewers at one admin-controlled inventory of AI provider connections—named, described, and scoped—instead of chasing keys pasted across automations and personal notes.
Configure a single OpenAI or Anthropic connection and let every AI Field Agent that drafts control narratives, summarizes assessments, or classifies findings consume it—no per-automation key handling by compliance teams.
If a provider incident or policy change demands it, disable the affected connection centrally and every dependent AI workflow stops at once. It's a resilience control you can execute in seconds—and demonstrate to reviewers afterward.
Pair Workspace Secrets with Service Accounts: governed identities for what touches SmartSuite, centrally stored credentials for the AI providers those governed workflows call.
Workspace Secrets is the Secrets page under Workspace Administration, where administrators store the API keys, access tokens, passwords, and connection strings that scripts and integrations use. Each value is encrypted on save, masked in every list, and referenced by name instead of being pasted into code. It replaces the former Workspace Secrets tab inside Script Engine.
Workspace Administrators, from Workspace Administration > Secrets. The page lists every secret with its name, a Used in count showing how many places reference it, and a masked value that shows only the last four characters. Secrets are created, edited, revealed, and deleted from that page.
A script declares the secrets it needs by mapping an environment-variable name to a secret in its definition, then reads the value from context.secrets at run time—for example, context.secrets.WEATHER_API_KEY. The script stores only the reference; the value is injected when it runs and is never saved with the script. A script sees only the secrets it declares, and saving fails if it references a secret that does not exist.
Only through Reveal. Lists and the Edit modal show a masked value with the last four characters, and Reveal is a two-step action that records the member's name and the time, which Administrators can review. The full value then appears in a read-only field with a Copy button.
Choose Edit on the secret and replace its value. The new value is encrypted on save and takes effect everywhere the secret is referenced, so every dependent script and integration picks it up without being updated one by one. Renaming a secret does not break dependents either, because the name is only a label.
SmartSuite warns you, lists every dependent script and integration by name and type, and turns each one off before removing the secret. If a dependent cannot be turned off, the deletion stops, so nothing keeps running against a missing value. The action cannot be undone, so replace the value instead when you are rotating rather than retiring a credential.
The help center does not gate Secrets to a plan. The page sits under Workspace Administration beside Script Engine, whose Scripting article lists all plan types. Check the pricing page for the current plan details of the scripts and integrations that consume secrets.
Put Every Credential Behind One Governed Door
Store API keys and tokens once, reference them by name in scripts and integrations, and rotate them without touching a line of code.