



Understanding GRC Metrics: Measuring Your Compliance Performance

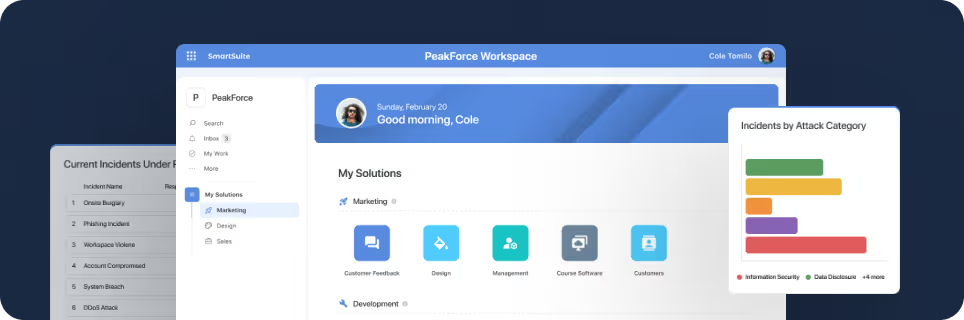
SmartSuite provides work platform for standardizing workflows in the following areas:
-
Governance, Risk & Compliance
-
IT & Service Ops
-
Project / Portfolio Management
-
Business Operations

Organizations today face an increasingly complex regulatory environment, with new laws and regulations constantly being introduced at both the national and international level. As a result, businesses must prioritize compliance efforts in order to avoid costly fines and reputational damage. However, measuring compliance performance can be challenging, as there are many different factors to consider. In this article, we'll explore the concept of GRC metrics and how they can help organizations better measure and manage their compliance efforts.
What are GRC Metrics?
GRC metrics are a set of measurements used to track and monitor an organization's governance, risk, and compliance (GRC) performance. These metrics can help businesses assess their compliance efforts and identify areas for improvement. GRC metrics can be broken down into several different categories, including:
- Governance metrics, which measure the effectiveness of an organization's governance framework and processes.
- Risk metrics, which measure the organization's risk exposure and the effectiveness of risk management controls.
- Compliance metrics, which measure the organization's compliance with applicable laws and regulations.
Why are GRC Metrics Important?
GRC metrics provide businesses with a way to measure and monitor their compliance performance over time. By tracking key performance indicators (KPIs), organizations can identify areas for improvement and take proactive steps to address compliance gaps. GRC metrics can also help organizations demonstrate their compliance efforts to stakeholders, including regulators, customers, and investors. By providing evidence of compliance, organizations can build trust and enhance their reputation. In addition, GRC metrics can help businesses identify emerging risks and adjust their compliance strategies accordingly. By monitoring key risk indicators (KRIs), organizations can stay ahead of potential threats and take action before they become problems.
What are examples of GRC metrics?
There are many different GRC metrics that organizations can track, depending on their specific compliance requirements and risk profile. Some common examples include:
- Compliance rate: This metric measures the percentage of compliance requirements that are being met by the organization.
- Risk exposure: This metric measures the level of risk exposure facing the organization based on factors such as industry, geography, and regulatory requirements.
- Incident rate: This metric measures the frequency and severity of compliance incidents, such as data breaches or safety violations.
- Training effectiveness: This metric measures the effectiveness of the organization's compliance training programs.
- Vendor risk: This metric measures the level of risk posed by the organization's vendors and suppliers.
Implementing a GRC Metrics Program
Implementing a GRC metrics program requires careful planning and coordination. Organizations must identify the key compliance requirements and risks facing their business and then select the appropriate metrics to track. In addition, organizations must establish processes for collecting, analyzing, and reporting GRC metrics. This may require the implementation of new technology solutions, such as GRC software, to automate the process and ensure accuracy. Finally, organizations must establish clear roles and responsibilities for GRC metrics, ensuring that relevant stakeholders are involved in the process and that accountability is established.
Measuring compliance performance is essential for businesses operating in today's complex regulatory environment. GRC metrics provide a framework for organizations to track and monitor their compliance efforts, identify areas for improvement, and build trust with stakeholders. By implementing a comprehensive GRC metrics program, organizations can better manage their compliance risks and enhance their overall performance.
To view a listing of GRC workflows that are supported by SmartSuite, please visit: SmartSuite's GRC solutions
Frequently Asked Questions
GRC metrics are measurements that help an organization track its performance in governance, risk management, and compliance. These metrics provide insights into the effectiveness of an organization’s governance frameworks, risk management controls, and compliance with legal and regulatory requirements.
GRC metrics are crucial because they allow organizations to monitor their compliance performance, identify areas needing improvement, and demonstrate compliance efforts to stakeholders like regulators and investors. These metrics also aid in managing emerging risks and adjusting compliance strategies proactively.
Common GRC metrics include the compliance rate, which measures how well the organization meets regulatory requirements; risk exposure, which assesses the level of risk the organization faces; incident rate, tracking the frequency and severity of compliance incidents; and training effectiveness, evaluating the impact of compliance training programs.
By tracking specific metrics, organizations can pinpoint compliance gaps, measure the effectiveness of their compliance programs, and make informed decisions to enhance governance and risk management practices. This proactive approach helps in minimizing risks and ensures continuous compliance with evolving regulations.
Implementing a GRC metrics program involves identifying key compliance requirements and risks, selecting relevant metrics, and setting up processes for data collection, analysis, and reporting. This often requires integrating GRC software to automate processes and maintain accuracy.
Technology, especially GRC software, plays a pivotal role in managing GRC metrics by automating data collection, facilitating complex analyses, and enabling real-time reporting. This helps organizations stay compliant and responsive to changes in the regulatory environment.
GRC metrics help organizations assess and manage risk by providing data on current risk exposures, trends in compliance incidents, and the effectiveness of risk controls. This enables proactive risk management and helps prevent issues before they escalate.
For practical examples of GRC workflows and how metrics are integrated, you can visit SmartSuite's GRC solutions page. This resource offers insights into various GRC metrics applied across different industries and organizational contexts.
These FAQs should help articulate the importance and implementation of GRC metrics for your blog post, enhancing its SEO and providing valuable information to your readers.
Put these ideas to work
Start a free trial, or book a demo and see how it runs in SmartSuite.

